Product Updates

Engine
Surface
AI Workflows
Area
Release Status

Showing 1 - 10 of 22 updates

Python 3.15 support is now available

General availability

We're happy to announce that we now support Python 3.15. Following its release on October 9, 2026, this support is now generally available (GA). You can now scan your Python 3.15 projects using both the command line interface (CLI) and your source control manager (SCM) integrations.

Python remains one of the most popular and widely used development ecosystems today. To continue supporting the Python community, Snyk now enables you to scan and secure your projects using the latest version of Python.

You can now import and scan your Python 3.15 projects from the CLI or your connected SCM. Please remember: if your project does not have a Python version specified, you need to configure it in the UI to use Python 3.15.

To learn more, visit Snyk for Python in our user documentation.

Headshot of Johann Sutherland

Johann Sutherland

Snyk Code October update

Improved

This update will be available on October 26, 2026.

Snyk Code reports significantly more findings in this update. Affected projects will report the additional findings on their next scan.

Snyk Code now analyzes more deeply and more accurately in Java, Kotlin, Go, TypeScript, JavaScript, Python, C#, PHP and Ruby.

Go, TypeScript and JavaScript

Snyk Code reads the Project's own configuration to resolve imports. For Go, it reads go.mod, which defines the module path that a project's packages import each other through. For TypeScript and JavaScript, it reads tsconfig.json and jsconfig.json, which define path aliases.

As a result, Snyk Code now analyzes these projects more accurately and with greater depth.

PHP

Snyk Code corrects boolean typing in PHP analysis. Previously skipped findings now appear across cross-site scripting, path traversal, SQL injection and other checks.

Java

Coverage is added or improved for these libraries:

  • Spring Data MongoDB

  • AWS SDK for Java, DynamoDB

  • AWS SDK for Java 2.x, DynamoDB

  • AWS SDK for Java 2.x, DynamoDB Enhanced Client

  • Apache Commons FileUpload

  • Google Cloud Big Query

Snyk Code adds a Mass Assignment rule for Spring applications. It reports request data that binds directly onto a database entity. Path traversal detection is wider.

More detection

Snyk Code reports additional findings in these areas:

  • Python: XML external entity injection.

  • JavaScript: deserialization, XML external entity injection and zip slip.

  • JavaScript, Bootbox: DOM-based cross-site scripting.

  • JavaScript, d3: DOM-based cross-site scripting.

  • C#: path traversal.

  • Go: SQL injection.

  • Go, AWS SDK for Go v2: path traversal through S3 object keys.

  • Ruby: path traversal, and a new server-side request forgery rule.

Template file analysis and serverless analysis

Snyk Code analyzes template files and serverless applications more accurately and with greater depth, building on the September update. Both will yield additional findings in projects that use template engines or serverless frameworks.

Learn more in the Snyk Code documentation.

Snyk secrets scanner reaches general availability

New

Starting August 4, 2026, Snyk secrets scanner is generally available to help secure your entire SDLC against credential leaks.

Stolen credentials remain a leading initial access vector in security breaches, and the rise of AI-generated code increases the risk of exposing sensitive data. You can now use Snyk secrets scanner to detect hardcoded credentials, API keys, and tokens across your repositories and prevent them from reaching commits or being leaked.

Key capabilities include:

  • Machine learning driven detection and prevention across your development surfaces.

  • Secrets detection for both human-written and AI-generated code.

  • Governance and finding management directly within the Snyk web UI.

For more information, please read the blog and Snyk Secrets documentation

Announcing Agent Fix: New Agentic Workflow & Model Upgrade

Improved

New Model & New Architecture

We're happy to announce we're upgrading Agent Fix to use the Claude family of models enhanced by Snyk's tooling and intelligence. This move delivers the following major improvements:

Security & Functional Enhancements

  • Agentic Retries: Our new workflow now detects where code suggestions deviate from security best practices. Instead of discarding the result, the system analyzes the failure and injects tailored guidance into the agent's subsequent attempts. 

  • Dynamic Few-Shot Prompting: We now use the same training set used to fine-tune our internal model to dynamically provide secure fix examples for the new model to follow. 

Expanded Support

  • Full Language Coverage: We will enable support for all Snyk Code languages on Day 1, removing previous limitations on language availability.

  • Comprehensive Rule Support: AI-powered fixes are now available for all supported rules and vulnerability types across the platform.

Measurable Impact

  • Golden Test Benchmark: Both Sonnet 4.6 and Opus 4.6 saw improved performance against Snyk’s Golden Test benchmark (72.4% to 82.5% and 74.6% to 85.4% respectively) with this new architecture vs. the models on their own.

Check out the blog for more details. This update started rolling out on May 26th and will reach 100% by end of day on May 28th.

David Alessi | Staff Product Manager

PR check report is now generally available

General availability

We’ve moved the pull request (PR) check report to general availability (GA). This update includes several enhancements to help you track how your teams adopt security scanning within their workflows. We added Snyk Code errors to the error PR checks, fixed historical calculation discrepancies in adoption metrics, and optimized the underlying tables so that all reporting components load and filter much faster. Additionally, we updated the display of source code manager (SCM) icons to better organize the PR scanning adoption by organization table, and we added PR check data to the Export application programming interface (API), enabling you to programmatically export this information.

We want to provide a reliable, high-performance way for you to verify that security checks are consistently running across your repositories. By moving this to GA, optimizing data loading, and providing API access, we ensure you have accurate, trendable metrics to measure the health of your application security (AppSec) program whether you are using the Snyk Web UI or your own internal reporting tools.

You can now filter and trend PR check adoption metrics by date to see progress over time. If you use GitLab, you will see a notification regarding data prior to February 5, 2025. When viewing the PR scanning adoption by organization table, you will notice a cleaner interface with updated source code manager (SCM) badges. Additionally, you can now automate your reporting workflows by pulling PR check data directly through the Export API.

To learn more, visit Pull Request check reporting in our user documentation.

Headshot of Sara Meadzinger

Sara Meadzinger | Staff Product Manager

PR Checks Report is now available in Early Access

Early access

We’re excited to announce the Early Access launch of the PR Check Report, a powerful new way to see how PR checks are performing and driving security outcomes across your organization. This release sets the stage for measuring the true security impact of PR checks across your organization and strengthening your overall prevention posture.

The current release of the report helps you:

  • Monitor performance: Track pass, fail, error, and marked-as-successful rates over time across Snyk Open Source and Snyk Code checks. 

  • Measure coverage: Understand where PR checks are enabled across your repositories to identify adoption gaps.

  • Uncover recurring errors: Surface common error types and configuration issues to improve scan reliability and developer confidence.

Feature highlights:

  • Flexible filters by time window, Snyk product (Snyk Open Source / Snyk Code), and project parameters like origin (SCM) and asset class.

  • Org, Group, and Tenant-level insights into PR check performance and coverage.

  • Export options for deeper data exploration and sharing.

The report is available under Analytics in the All Reports section for Tenant-level visibility. You can also find it in the Reports section of your Group or Organization by selecting Pull Request Checks Usage & Performance from the Change Report menu.

Learn more in our user documentation and connect with your account team to share feedback or help shape upcoming improvements.

Headshot of Mayank Khera

Mayank Khera | Senior Product Manager

Snyk Agent Fix in PRs is now available for GitLab and Azure Repos

Early access

This feature eliminates the manual overhead of resolving vulnerabilities, helping developers merge secure PRs faster while integrating seamlessly into their existing workflows. With Snyk Agent Fix, developers are empowered to act immediately on SAST findings by generating and applying fix suggestions directly within pull requests, reducing context switching and streamlining remediation.

The following capabilities are supported for Early Access:

  • Generate fix suggestions using @snyk /fix command in a PR inline comment, displaying a proposed code change.

  • View and explanation of the suggested fix alongside the code snippet.

  • Apply the suggested code directly to the PR as a commit using the @snyk /apply command.

  • Generate multiple fix suggestions within the same PR, where applicable.

If you'd like to enable this feature for your organization, you can do so in the Pull Request Experience section in your SCM integration settings.

Check our user documentation for more details and connect with your account team to participate in feedback sessions to shape the future of your workflows with Snyk.

Headshot of Mayank Khera

Mayank Khera | Senior Product Manager

Redesigned summary comments for pull requests

Improved

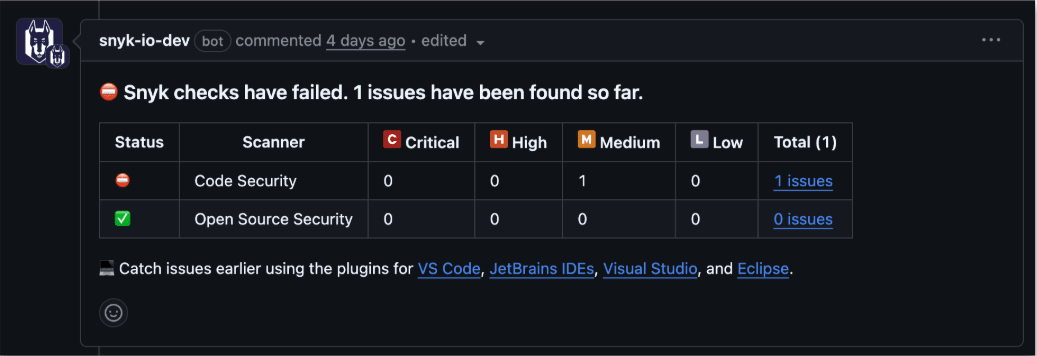
We're excited to introduce a new design for PR summary comments, which will give developers and reviewers a clearer, more organized view of their PR check results.

  • Streamlined summaries: Results are now displayed in a simple table, with links to the full test report and the number of issues per scan type. This helps teams quickly see whether a PR includes open-source vulnerabilities, license issues, or code vulnerabilities, and then dive deeper into the details in Snyk.

  • Cleaner experience: The banner has been removed, making it easier to see PR check results at a glance, even if they're being consumed by other integrations (like Slack notifications).

The new design for summary comments is enabled by default, and is available across all supported SCMs.

Summary content table with columns for Status, Scanner, Critical, High, Medium, Low, and Total vulnerabilities

We're excited to see how this helps your teams streamline code reviews and address issues more efficiently!

Headshot of Mayank Khera

Mayank Khera | Senior Product Manager

GitLab customers can now reliably gate merges with Snyk PR checks

Improved

We're excited to share an improvement to our GitLab integration that ensures Snyk's Pull Request (PR) Check status always reports to the correct pipeline.

Previously, the PR Check status could appear on the wrong pipeline, especially with Merged Result Pipelines. This sometimes prevented GitLab's "Pipelines must succeed" feature from working correctly, potentially alowing insecure merges. With this update, you can now confidently set branch protection rules with Snyk PR Checks and merge with peace of mind.

  • Enforce secure merges with confidence: Snyk PR Check status now correctly attaches to the highest-priority pipeline (Merge Result, Merge Request, or Branch). This ensures GitLab's merge gate always has Snyk scan results, so vulnerable code can be blocked reliably.

  • Improved clarity for developers: The Snyk status now attaches to the right pipeline, removing confusion about which pipeline reflects the security scan.

This improvement has been rolled out to all customers today, and no explicit action is required. For more details, check our user documentation.

Headshot of Mayank Khera

Mayank Khera | Senior Product Manager

PR Experience for Gitlab, Azure Repos, and BitBucket Server is now Generally Available

New

We’re pleased to announce that Issue Summary Comments and High-Context Inline Comments are now live and enabled by default for all customers using PR Checks with the following Source Code Manager (SCM) integrations:

  • GitLab

  • Azure Repos

  • Bitbucket Server


What’s included:

  • Issue Summary Comment for both successful and failed PR checks, covering Snyk Code and Open Source security & license findings.

  • Inline Comments for Snyk Code findings, providing high-context feedback directly in the pull request.


To adjust your preferences, head over to Integration Settings in the Snyk UI where you can toggle comments on or off at any time. This release is a big step forward in our mission to make security native to the developer experience. Refer to the user documentation for more details.

Headshot of Mayank Khera

Mayank Khera | Senior Product Manager